LEVEL 15 OF 18
Advanced Offensive Security
Specialize in penetration testing and red teaming in controlled labs.
Study advanced authorized assessment, red-team planning, adversary simulation and professional reporting in MentorPulse cybersecurity Level 15.
Recommended preparation: Level 14: Security Engineering. This public overview does not expose private learner records or require a login.
Cybersecurity skills and career relevance
Develop professional assessment planning and evidence communication in controlled environments.
The 18-level roadmap describes the full learning path. Published lessons, labs and projects are available in the app; remaining curriculum content is still in development. Access varies by plan.
Curriculum topics
- Advanced reconnaissance
- Advanced web exploitation
- Privilege escalation
- Active Directory attacks
- Exploit development
- Lateral movement
- Command-and-control concepts
- Evasion concepts
- Adversary simulation
- Red-team operations
- Reporting
- Purple-team collaboration
Level 15 module outline
- 1.Advanced penetration testing methodology
- 2.Advanced reconnaissance
- 3.Advanced network assessment
- 4.Advanced web assessment
- 5.Exploit-development concepts
- 6.Privilege escalation research
- 7.Adversary simulation
- 8.Red-team operations
- 9.Command-and-control concepts
- 10.Professional penetration testing
This is the planned module outline, not a claim that every lesson position has been published.
Practice and portfolio directions
- Conduct a complete authorized red-team simulation in a controlled lab.
Project directions come from the roadmap. Availability and requirements for individual exercises are shown in the signed-in learning workspace.
Related learning screenshots
Historical interface examples; publication counts and learner progress may differ from the current app.
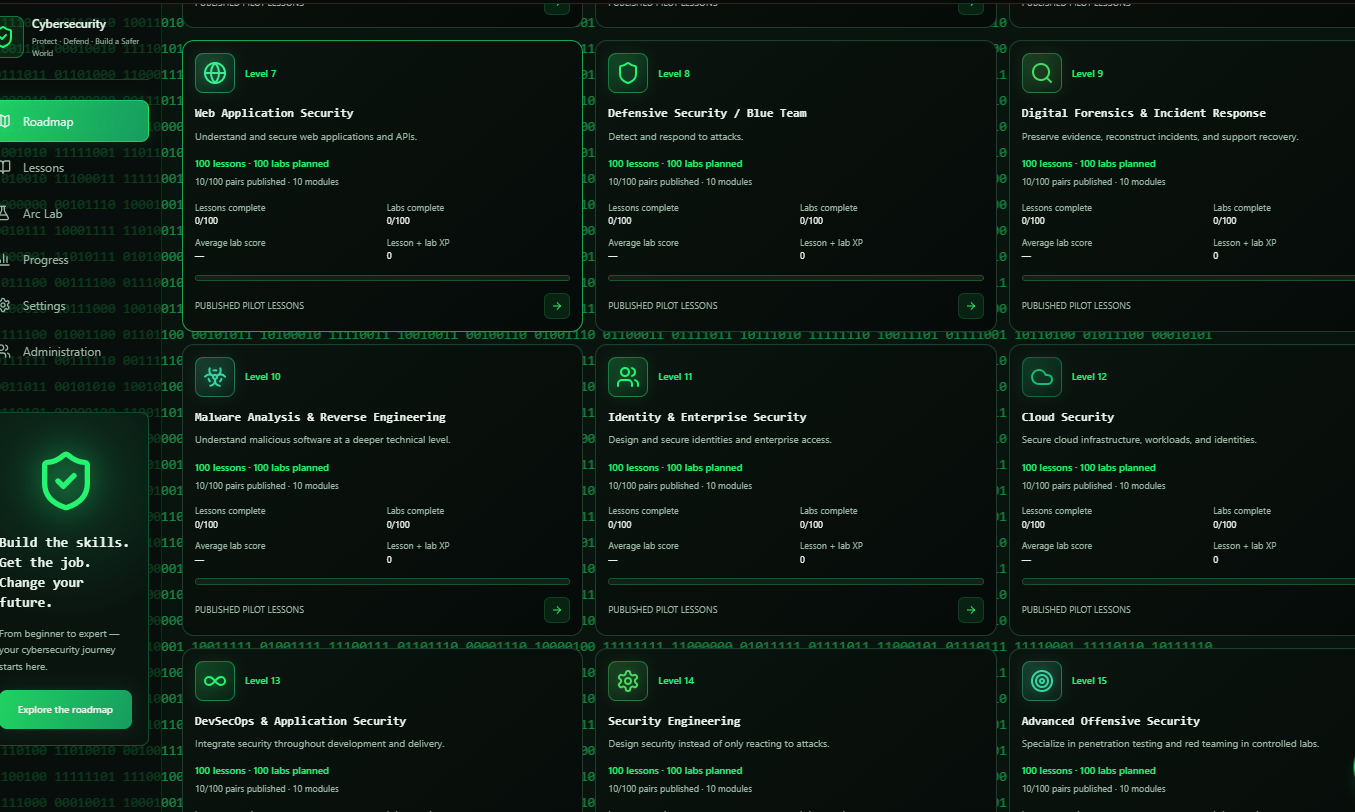
Cybersecurity roadmap: professional specializations
Professional study areas connect web and enterprise security with investigation, cloud and engineering.
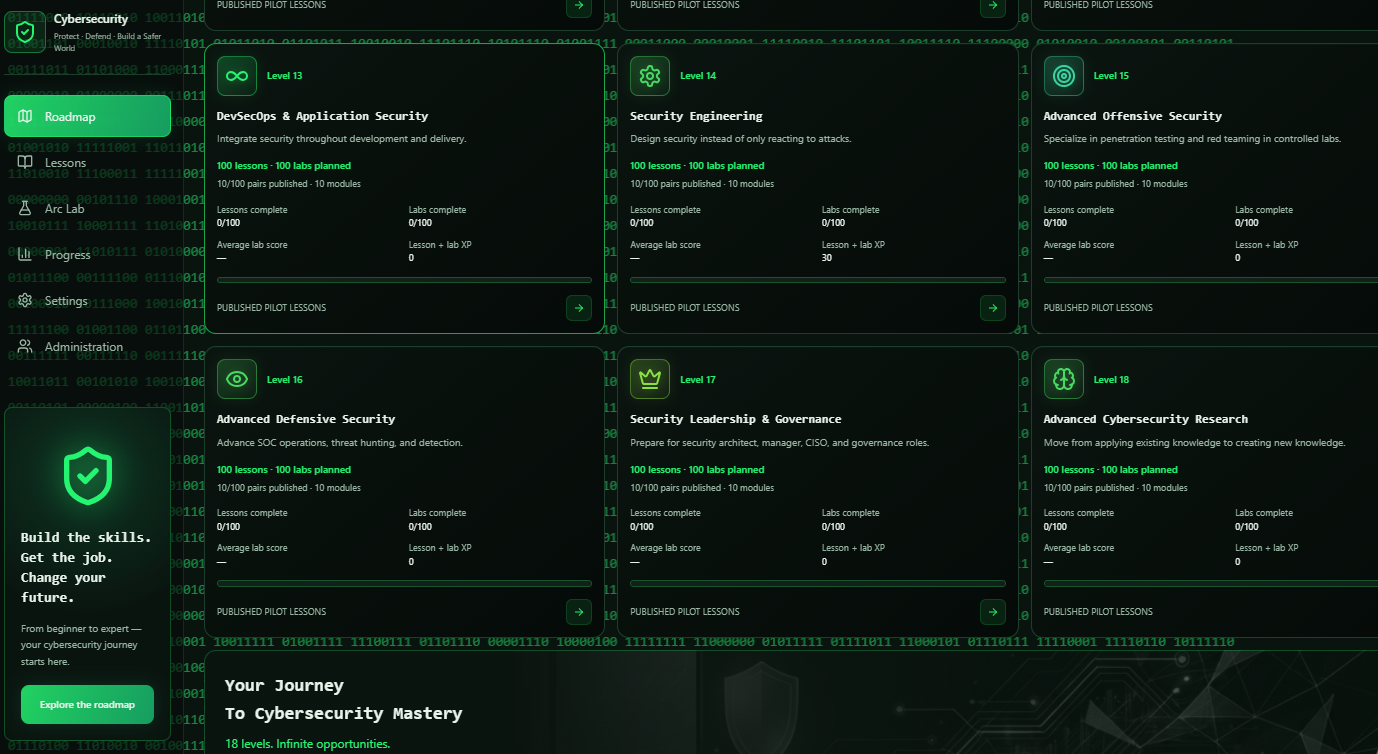
Advanced cybersecurity learning roadmap
Advanced roadmap areas focus on development, architecture, operations, governance and research.
Cybersecurity education and career development, not a certification, accreditation or employment guarantee. External tools and learning resources are referenced for study, not as partnerships. Practice only in isolated environments or with explicit authorization.